

JWF-SecureClient
In addition to test results, modern production environments increasingly generate and process security-critical information such as cryptographic keys, vehicle and component identities, flash content, and logistics registrations. At the same time, regulatory requirements such as the EU Cyber Resilience Act (CRA) are increasing demands on data security, traceability, and system integrity.
JW Froehlich Maschinenfabrik GmbH
Team Digital Solutions
sales@jwf.com
+49 711 79766-752
The JWF SecureClient acts as the central security instance within the production IT environment, consolidating security-critical functions in a controlled system architecture. Operations such as key generation, challenge-response calculations, and flash data encryption are executed exclusively within the protected server core.
Security Functions
- Centralized key generation and key management
- Secure transfer of master keys to the test computers
- Server-side encryption of flash data
- Secure logistics integration with asymmetrically encrypted data exchange
- Process interlocking in the event of missing registration
Typical production line risk scenarios
- Decentralized test stations can become points of attack and compromise security-critical processes.
- Unencrypted or insufficiently protected flash content carries the risk of targeted industrial espionage.
- Cryptographic keys may be intercepted or misused if central control or adequate protection is lacking.
- Missing or incorrect logistics registrations can jeopardize the integrity of production processes.
- Insufficient documentation makes it more difficult to provide evidence and demonstrate compliance during audits and regulatory inspections.
The JWF SecureClient mitigates these risks through a clearly defined Trusted Security Zone and centralized server-side control of security-critical processes.
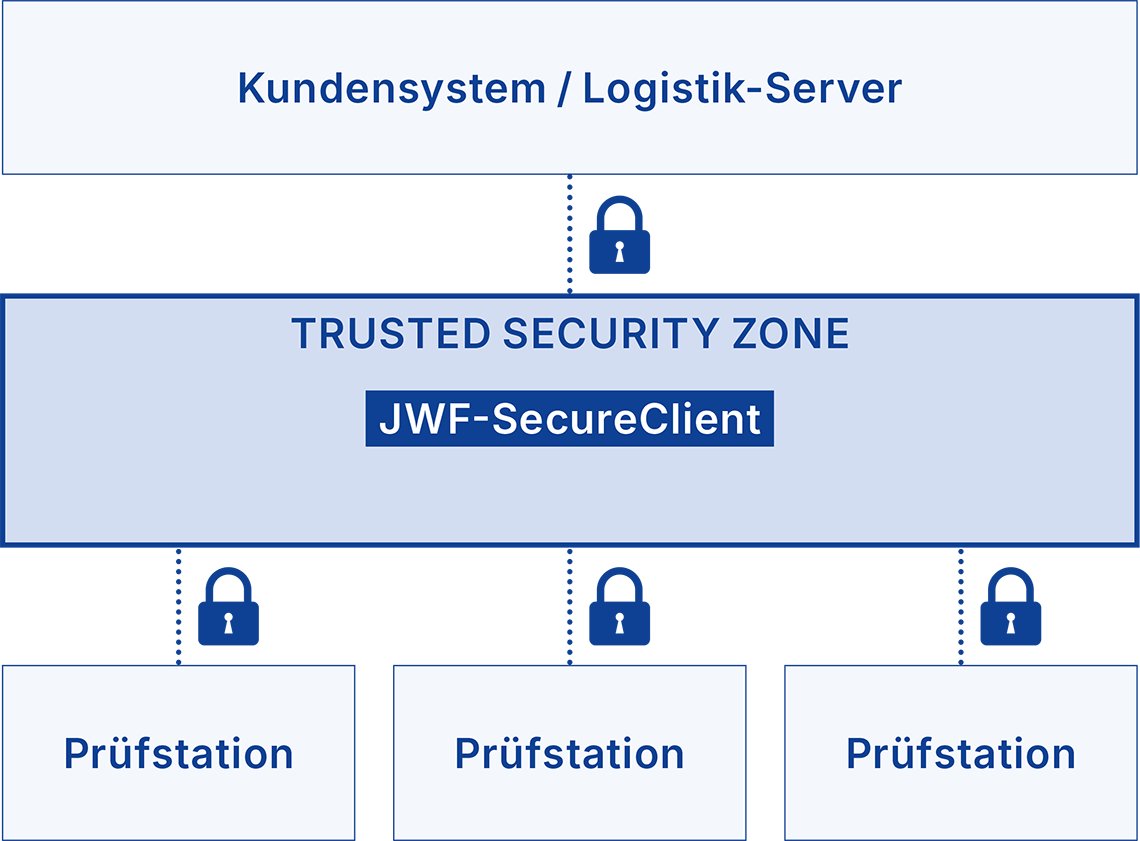
Technical Highlights
Tamper-Proof Key Management
Secure execution of the standardized AUTOSAR948 process for Secure Hardware Extensions (SHE).
Challenge-Response Calculation in the Server Core
Master keys remain protected within the JWF SecureClient.
Asymmetrically Secured Logistics Integration
For example via OpenPGP, ElGamal, and SHA-512.
Process Interlock
A test specimen only leaves the test field after validated feedback from the customer system has been received.
Integration of Customer-Specific Software
Secure handling of sensitive customer data within a protected server environment.
Your Benefits
| Safe | Protection of your intellectual property |
|---|---|
| Resistent | Protection against production tampering |
| Conform | CRA compliance |
| Reduced | Reduced vulnerability |
| Integrable | Seamless integration into existing IT structures |